
Table of Contents
Coverage applications now require proof that controls are working, not just purchased. Your broker may ask for access control records, backup reports, firewall settings, monitoring alerts, incident response notes, vendor approvals, and employee training logs before renewal moves forward.
Willis Cantey, CEO at Cantey Tech Consulting, notes: “Treat every insurer question like an operations request, because the answer should come from tickets, logs, approvals, restore tests, and training records you can verify.”
That is where a cyber insurance coverage checklist becomes practical. At Cantey Tech Consulting, we connect cybersecurity planning with the evidence insurers ask for, built from 15+ years supporting business IT and cybersecurity. Claims frequency rose 12%, while 72% of senior technology leaders say they are only somewhat confident in their coverage. For 82%, the value is financial protection. Proof matters.
Cyber Insurance Coverage Checklist For Controls Insurers Expect To See
Underwriting scrutiny now reaches into how your safeguards run each week. Insurers often ask for operational proof, especially when 59% of CISOs say insurers pushed them to implement at least one cybersecurity solution they were not previously considering.
These controls reduce claim disputes and limit disruption when a user, endpoint, or vendor workflow comes under review.
-
Multifactor access controls: Track MFA for admin accounts, remote access, and privileged users. Keep approval records when finance, HR, or a branch manager requests elevated access.
-
Verified backup recovery: Document backup frequency, test restores, ransomware resilience settings, and recovery notes. Claims frequency rose 12%, so a successful restore of the accounting share is stronger than a checkbox.
-
Firewall and endpoint protection: Maintain firewall management records, EDR alerts, device security status, and response notes when malware detection or patch issues appear.
-
Employee security training: Keep phishing awareness results, password behavior follow-ups, and repeatable training records. Social engineering accounts for 42% of incurred claims and 88% of incurred losses.
We tie technology, training, and process improvement together so these records support the policy review process that comes next.
Cyber Insurance Coverage Policy Requirements That Affect Daily Operations
Insurance requirements affect more than a renewal form. They shape ticket queues, onboarding, offboarding, purchase approvals, and vendor risk reviews because 78% of senior technology leaders say IT or security leads cyber insurance management. When cyber insurance coverage policy requirements land on your desk, the real work becomes proving who approved access, when an account was removed, and whether backup recovery was tested. Only 17% say they are very familiar with third-party liability coverage, so clean records help reduce confusion.
A multi-location medical office preparing renewal documents may need the new employee access approval from HR, the terminated employee account removal ticket, last month’s backup restore report, a firewall rule review for a billing vendor, and phishing training completion records for front desk staff. If one item lives in email, another in a spreadsheet, and another inside a firewall console, renewal prep becomes a scavenger hunt. Clean records save time.
At Cantey Tech Consulting, we support 350+ clients with over 15 years of experience and a 75% first-call resolution rate, which helps when local, in-house support needs to gather evidence and close gaps before a deadline.
Cyber Insurance Coverage And Policy Requirements For Evidence Readiness
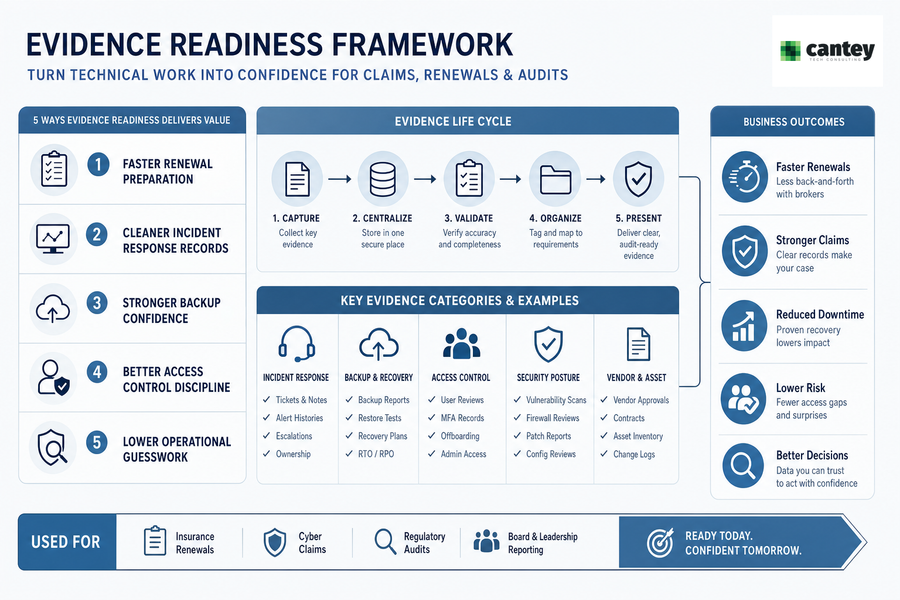
Evidence readiness matters when a claim, renewal, or audit turns yesterday’s technical work into today’s business decision.
-
Faster renewal preparation cycles Centralized records reduce last-minute requests from brokers. You spend less time chasing backup screenshots, MFA exports, and vendor approval emails.
-
Cleaner incident response records Ticket notes, alert histories, and escalation steps show what happened and when. Cantey Tech Consulting service desk KPIs support clear response tracking, ticket ownership, and escalation records leaders can review during an event.
-
Stronger tested backup confidence Tested restores reduce downtime because your team already knows which systems recover first. A documented restore of payroll, file shares, or customer records proves recovery capability.
-
Better access control discipline User reviews, MFA checks, and offboarding tickets reduce account misuse. This matters when a departed employee still has VPN access or a shared admin login appears in an audit.
-
Lower operational guesswork risk Monitoring, vulnerability testing, and firewall reviews reveal gaps before insurers or attackers do. Cantey Tech Consulting helps turn technical activity into business-ready documentation your leadership team can use.
Strengthen Your Cyber Insurance Readiness
Cyber Insurance Coverage Items For Security Maturity
Improving insurance readiness requires coordination across leadership, IT, finance, HR, and department managers. Trying to fix every control at once creates missed approvals and noisy ticket queues, so staged improvements work better. Insurers influence roadmaps too, since 59% of CISOs say insurers pushed them to implement at least one cybersecurity solution they were not previously considering. Start with the items that reduce support requests, protect customer data, and speed recovery.
-
Review current security tools: Compare network security, EDR, email security, MDM, patch management, and next-gen firewalls against insurer questions. This helps you find overlap, gaps, and tools that are installed but not fully used.
-
Confirm backup recovery: Verify backups are running and restore tests are documented. Finance and operations need proof that invoices, payroll data, and shared files can be restored.
-
Tighten access steps: Review MFA, admin access, VPN access, and offboarding. Clean approvals reduce account misuse and help HR close the loop on terminations.
-
Run vulnerability testing: Prioritize remediation by business risk, not just scan severity. Customer-facing systems and remote access deserve fast attention.
-
Schedule awareness training: Track cyber awareness training completion, especially since social engineering accounts for 42% of incurred claims and 88% of incurred losses.
When internal teams are stretched, Cantey Tech Consulting can support a co-managed IT model across remote monitoring, firewall management, backup recovery, and incident response.
Strengthen Your Renewal Readiness
Turn insurer requirements into documented controls. Cantey Tech Consulting helps you prepare the evidence your policy review may demand.
Cyber Insurance Coverage Policy Steps To Strengthen Renewals
Insurance readiness improves renewals, claim response, daily security habits, and operational resilience because your controls are documented where people actually work: tickets, approvals, alerts, backup reports, and training records. With 72% of senior technology leaders only somewhat confident in their current cyber risk coverage, clear evidence gives your team a stronger position before renewal pressure starts.
Cantey Tech Consulting helps you align cybersecurity planning with evidence insurers can review through tailored cybersecurity planning, proactive threat detection, backup and disaster recovery, firewall management, vulnerability testing, cyber awareness training, rapid response, and 24/7 support. Contact Cantey Tech Consulting when you want one vendor, one invoice, and practical help from in-house teams backed by 15+ years of experience, 350+ clients, a 75% first-call resolution rate, and end-to-end IT support across tools, data, people, process, and strategy.